Mastering AI GRC
Technology, Risk, Security and Compliance in the Age of Intelligent Machines
A comprehensive guide to how AI works, where its risks come from, and how to govern, secure and audit it – from the history of the field to the latest standards and regulations, including a new end-to-end AI risk map.
Three books and a poster for every stage of AI GRC
Start with the Primer for the essentials, go deep with Mastering AI GRC, prepare for your next role with the Interview Q&A, and keep the Risk Map on the wall.
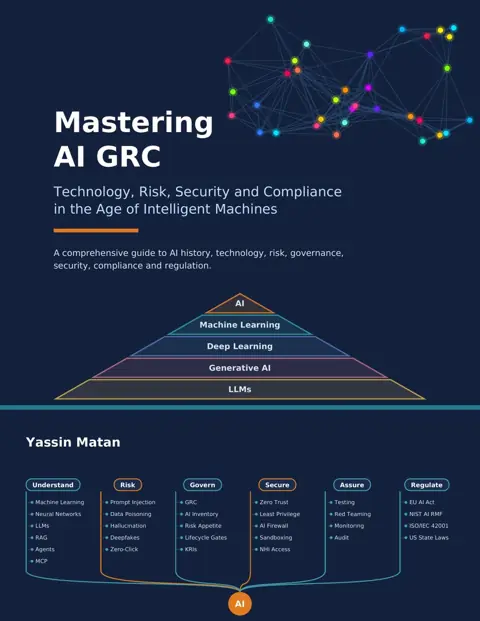
Mastering AI GRC
The flagship book: a single, comprehensive reference on artificial intelligence and how to govern, secure and audit it.
Explains how AI works – machine learning, large language models, retrieval-augmented generation, agents and the Model Context Protocol – and its history and pioneers. Then it covers AI risk in depth (security threats, data poisoning, zero-click attacks, fairness, frontier risks and a 36-risk end-to-end risk map), building an AI governance program, securing the enterprise AI environment, testing and monitoring, third-party risk, and the standards and regulations that apply worldwide, including a dedicated chapter for banks and financial institutions.
- Students and newcomers to AI and AI GRC
- Risk, compliance, audit and legal professionals
- Security, engineering and architecture teams
- Executives and board members who oversee AI
AI GRC Primer
A short, executive-level introduction to AI concepts, terminology, risks, governance, standards and regulations – designed to be read in an afternoon.
Condensed from Mastering AI GRC without history or technical depth. It gives the essential definitions, the main categories of AI risk, the building blocks of AI governance, the end-to-end risk map at a glance, and the frameworks and laws leaders need to know, including financial services requirements.
- Executives, senior managers and board members
- Business and product leaders sponsoring AI
- New team members who need a fast grounding
- Anyone who wants the essentials before the full book
AI GRC Interview Questions & Answers
Model answers to the questions asked in AI governance, risk, compliance and security interviews, with the most important questions first.
Starts with the top 25 questions asked in almost every AI GRC interview, then covers AI technology concepts, risks and security threats, rogue agents and platform controls, governance and controls, frameworks and regulations, financial services requirements, the end-to-end risk map, scenario and behavioral questions, and questions to ask the interviewer.
- Candidates for AI GRC, technology risk, audit and security roles
- Professionals moving into AI governance from adjacent fields
- Hiring managers building interview guides
- Students preparing for their first AI risk role
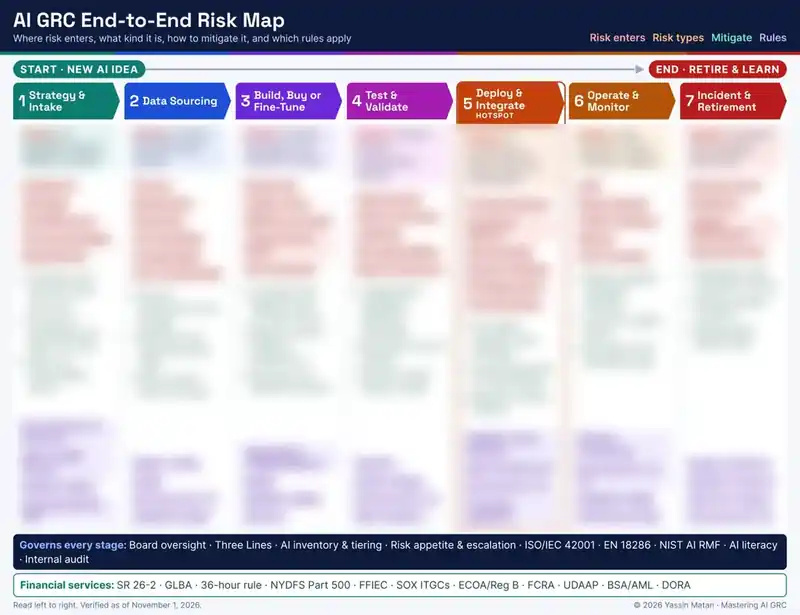
AI GRC End-to-End Risk Map Poster
The whole AI risk lifecycle on one wall: where risk enters, what kind it is, how to stop it and which rules apply.
Seven stages from a new AI idea to retirement, 36 risk types, the core controls and policies for each stage, the applicable standards and regulations, and a financial services overlay. It matches the risk map chapter of Mastering AI GRC and is current as of November 2026.
- Risk, audit, security and AI teams
- Training rooms and governance committees
- Offices and risk or security operations floors
- Readers of the book who want the map at a glance
Stay current on AI GRC
Get notified about new editions, regulatory updates, risk map revisions and new resources. One short email a month at most.